Two-factor authentication for money accounts
Not all second factors are equal. The difference between a texted code and a security key is the difference between slowing an attacker and stopping one.
On this page
- Two-factor authentication asks for proof from two different categories: something you know, something you have, or something you are.
- CISA ranks SMS and voice codes as the weakest option and FIDO-based security keys or passkeys as the strongest.
- Six-digit codes stop password-only attacks but can still be phished; security keys and passkeys are bound to the real website.
- Never approve a login prompt you did not start and never read a code to someone who calls you.
- 2FA protects accounts at companies; it does not protect a self-custody wallet whose seed phrase leaks.
Two-factor authentication (2FA) means logging in with two different kinds of proof, usually a password plus a code, an app approval or a physical key. For money accounts, US agencies rank security keys and passkeys strongest, authenticator apps in the middle, and SMS codes weakest.
What is two-factor authentication?
The Federal Trade Commission defines 2FA as needing credentials from two of three categories to log in:
- Something you know, such as a password, a PIN or a security answer.
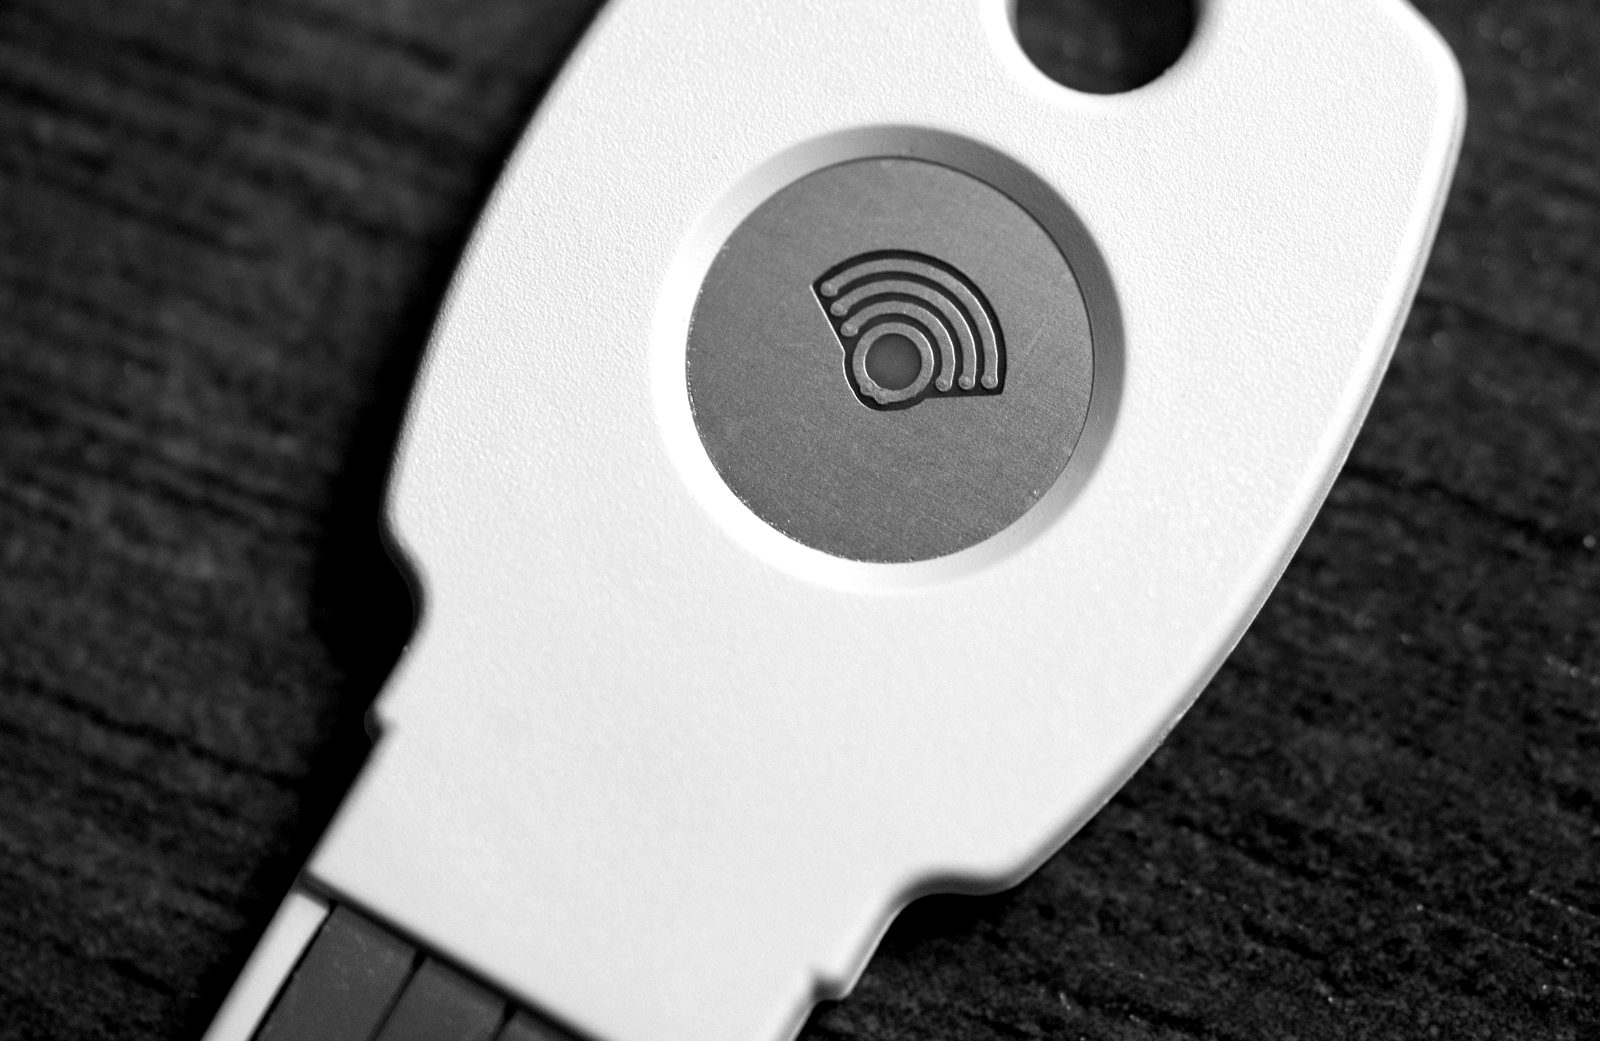
- Something you have, such as a one-time code sent by text or email, a code from an authenticator app, or a physical security key.
- Something you are, such as a fingerprint or your face.
The point is that one stolen secret is no longer enough. Passwords leak in data breaches and get typed into fake pages; a second factor of a different kind means the attacker also needs your phone, your key or your face. CISA puts it simply: weak or stolen passwords are a common way in for criminals.
For money accounts, such as a bank, a broker or a crypto exchange, 2FA is the minimum. It also matters for your email, because email is where password resets land.
Which type of 2FA is the most secure?
US agencies agree on the order. CISA's fact sheet ranks phishing-resistant methods first and SMS last; the FTC calls security keys the strongest option because they use no credential a hacker can steal.
| Method | How it works | Main weakness | Phishing-resistant? |
|---|---|---|---|
| SMS or voice code | A code sent to your phone number | SIM swaps and phishing; CISA says use only as a last resort | No |
| Email code | A code sent to your inbox | Only as safe as your email account | No |
| Push approval | Tap "Approve" in an app | "Push bombing": repeated prompts until you tap yes; number matching helps | No |
| Authenticator app code | A short-lived six-digit code generated on your phone | Can be typed into a fake site | No |
| Passkey or security key | Your device signs a challenge for the real site using FIDO standards | You must keep a backup method if the device is lost | Yes |
NIST's 2025 digital identity guidelines go further and label authentication over the phone network, meaning SMS and voice, as restricted, advising services to watch for SIM changes and number porting before trusting it.
Why can a code still be phished?
A one-time code proves you have the phone, but not which website you are typing it into. A phishing page can ask for your password and your current code, then pass both to the real site within seconds. NIST lists passwords, one-time codes and out-of-band approvals among authenticators that are not phishing-resistant.
Passkeys and security keys work differently. The FIDO Alliance explains that they use public-key cryptography and are bound to the specific website or app. A key registered for your bank's real domain will not produce a valid login for a lookalike domain, however convincing it looks.
How should you set up 2FA on your money accounts?
Start with your email. Whoever controls your inbox can reset most other passwords.
Then your bank, broker and any crypto exchange. Choose the strongest method each one offers: a passkey or security key first, an authenticator app second, SMS only if nothing else is available.
Use long, unique passwords. NIST's guidelines set a minimum of 15 characters for a password used on its own and drop forced complexity rules. Ethereum.org strongly recommends a password manager.
Plan for a lost phone or key. Register a second key or method where the service allows it, and store any backup codes offline, the way you would a seed phrase.
Remove SMS as a fallback once a stronger method is working, if the service lets you. A strong front door is weaker if a texted code still opens the side door.
What 2FA mistakes do beginners make?
- Approving a prompt you did not start. CISA describes push bombing: attackers who already have the password send prompt after prompt until the victim taps Approve. If you did not just try to log in, deny it and change the password.
- Reading a code to a caller. The FTC says some of the costliest impersonation scams start with a fake security alert, often claiming to be from your bank. Treat any caller who asks for a login code as an impostor: the code exists to prove that you, not they, are signing in.
- Treating SMS as strong. Ethereum.org says SMS-based 2FA is susceptible to SIM swapping and calls it not secure.
- Protecting the exchange but not the email. Reset links make your inbox the master key to everything else.
- Thinking 2FA protects a self-custody wallet. 2FA guards logins at companies. A wallet you control is guarded by its seed phrase and by what you sign; see hardware vs software wallets.
Questions readers ask
Is a passkey the same as two-factor authentication?
A passkey replaces the password with a cryptographic key on your device, usually unlocked by fingerprint, face or PIN. The FIDO Alliance says it combines something you have with something you are or know, though not every regulator lists it as MFA yet.
Is SMS 2FA better than nothing?
Yes. It still blocks attackers who only have your password. CISA calls it a last-resort option, so switch to an app, passkey or security key when one is available.
What is a SIM swap?
An attacker gets your phone number moved to a SIM card they control, so texted codes go to them. The FBI's IC3 logged 971 SIM-swap complaints in 2025.
What happens if I lose my security key?
You sign in with your backup method, such as a second key or another registered factor, then remove the lost key. Without a backup, you face the service's account-recovery process.
Turn on 2FA everywhere money lives, starting with your email. Prefer passkeys or security keys, accept authenticator apps, and treat SMS as a stopgap. Then remember the human side: treat anyone who asks you to read out a code, or to approve a login you did not start, as an attacker.
Sources
- US Federal Trade Commission, Use Two-Factor Authentication to Protect Your Accounts (2024)Primary source
- National Institute of Standards and Technology, SP 800-63B-4: Digital Identity Guidelines, Authentication and Authenticator Management (2025)Primary source
- Cybersecurity and Infrastructure Security Agency, Implementing Phishing-Resistant MFA (fact sheet) (2022)Primary source
- Cybersecurity and Infrastructure Security Agency, Require Multifactor AuthenticationPrimary source
- FIDO Alliance, PasskeysPrimary source
- ethereum.org, Ethereum security and scam prevention (2026)Primary source
- FBI Internet Crime Complaint Center, 2025 IC3 Annual Report (Internet Crime Report) (2026)Primary source
- US Federal Trade Commission, FTC Data Show People Reported Losing $3.5 Billion to Imposter Scams in 2025 (2026)Primary source
Educational content only — not financial, investment, legal or tax advice. Crypto-assets are high-risk and you could lose all the money you put in. Rules differ by country; check with your national regulator. See our risk disclosure and editorial policy.
Read next
- Security & Privacy · Intermediate
Phishing and address poisoning
Lookalike sites and lookalike addresses: how both scams work and the habits that defeat them.
- Security & Privacy · Beginner
Common crypto scams
Fake platforms, giveaways, impostors and recovery scams: how they work and the signs they share.
- Security & Privacy · Beginner
Seed phrases explained
What the 12 or 24 recovery words actually encode, and how to keep them out of reach.
- Security & Privacy · Beginner
Hardware vs software wallets
Online keys versus offline keys: the trade-off between convenience and exposure, explained.